Get Ahead of AI Threats to Your Personal Security
AI is accelerating digital threats. Strengthen your accounts, protect your home network and reduce the sensitive data you leave exposed.
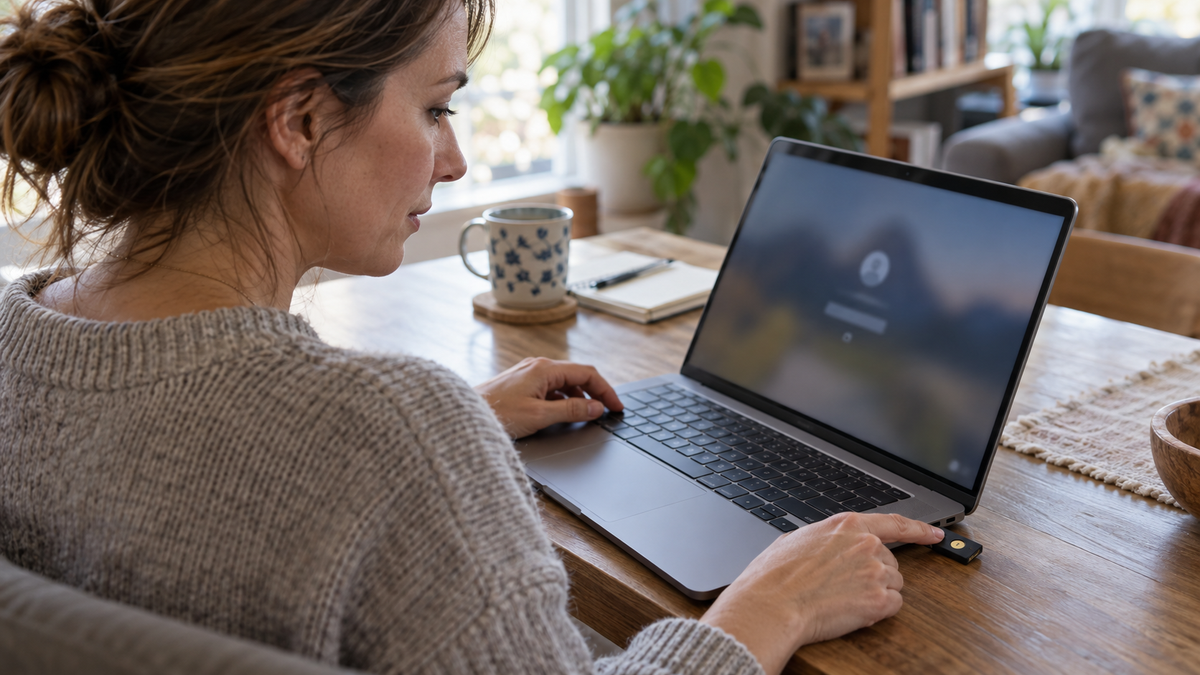
AI is giving attackers more ways to research targets, impersonate people and exploit vulnerable systems; the UK’s National Cyber Security Centre expects attacks to grow more frequent and intense. Waiting until an account is stolen or private files are exposed leaves you trying to recover under the worst possible conditions.
Every security measure involves tradeoffs, and what makes sense for one person may not suit another; the options below are starting points to weigh against your own risks, needs and comfort with technology. Frankly, the measures outlined here may not be enough as AI threats develop, but getting the basics right now could help limit the damage and will make it easier to adopt stronger protections if they become necessary.
Stronger account security
A password manager can help you create strong, unique passwords wherever they are still required, while two-factor authentication adds protection and phishing-resistant passkeys or hardware security keys offer stronger options where supported. SMS codes can be phished or intercepted through SIM-swapping, so alternatives worth considering include authenticator apps, email codes where offered and FIDO2 hardware keys; app and email codes can still be phished, email codes depend on inbox security, and recovery options deserve review before switching.
Hardware security keys
For email, password managers and other critical accounts, consider a FIDO2 hardware key such as a YubiKey: it resists fake login pages, adds protection when a password is stolen and keeps its private authentication keys on the physical device rather than exposing them to the website. A registered spare stored separately and a clear understanding of account recovery can reduce the risk of lockout, while the separate browser-session risks discussed below still need attention.
Special attention for email
Your inbox holds years of personal information and often controls password resets for other accounts, making it a particularly valuable target and a good place to prioritize phishing-resistant passkeys or hardware security keys. A review of signed-in devices, connected apps, forwarding rules, filters, delegated access and recovery details can reveal unwanted access; anything unfamiliar deserves investigation before you decide what to remove.
Stronger email protection
Google’s Advanced Protection Program is worth considering for stronger Google account security, with passkey or hardware-key sign-in and tighter controls on third-party app access and account recovery. The tradeoffs include restrictions on some apps, recovery that can take days and no downloadable backup codes, so understanding those limits and arranging a backup key or passkey and current recovery information matters before enrolling.
Browser session hijacking
Attackers are increasingly targeting the cookies that keep you signed in, allowing a stolen session to bypass another password or MFA check even when you originally used a hardware key. Browser and operating-system updates, fewer unnecessary extensions and caution with downloads can reduce exposure; if you suspect a compromise, the provider’s account-recovery guidance or trusted technical help can walk you through ending active sessions and securing the account from a clean device.
Timely security updates
AI is accelerating vulnerability discovery and helping defenders develop fixes faster: Google reports a sharp increase in security bugs fixed in Chrome through AI-assisted work. Automatic updates for your operating system, browser and apps can help those fixes reach you sooner, with required restarts scheduled promptly around your work and a plan to upgrade or replace software and devices that no longer receive security updates.
Mobile device security
Phones and tablets deserve their own security review, covering account protection, app permissions, updates, screen locks and theft protections, with important differences between platforms. Apple’s Personal Safety User Guide for iPhone and iPad and Google’s Android security guide are useful starting points, with features and settings varying by device, software version and region.
Home network protection
For more visibility and control, consider options such as Firewalla, with app-based device controls and suspicious-connection alerts or blocking, and Ubiquiti’s UniFi gateways, a more hands-on option with intrusion detection and prevention. Current firmware and ongoing security support matter whichever equipment you use; the manufacturer’s guidance or trusted technical help can clarify setup, whether remote administration is needed and when unsupported equipment warrants replacement.
Separating connected devices
Network separation can limit what a compromised camera, television or other connected device can reach by blocking unnecessary access to computers and storage; simply giving the network a different name isn’t enough. An isolated guest or device network may be worth considering, with guidance on your router’s settings because separation can also interrupt casting, printing or other connections you rely on.
What you keep in the cloud
Old tax documents, identity scans, private correspondence and shared folders are worth reviewing for sensitive copies you no longer need, with retention requirements and a verified backup of anything important checked before deletion. For files you keep, end-to-end encrypted services or encrypted local storage may be appropriate, provided you have a separate, tested backup and securely stored recovery keys.
Encryption and long-term exposure
AI’s advances in mathematics are raising alarms among cryptographers, and researchers have already demonstrated AI-assisted attacks on experimental cryptographic designs. Encryption and current software remain important protections, while retaining less unnecessary sensitive data can reduce long-term exposure: information stolen in encrypted form today could become readable if the protections it depends on are broken later.
Caution with vibe-coded software
AI-generated applications can inherit compromised dependencies or recommend packages that don’t exist, creating openings for supply-chain attacks. Before trusting an experimental application with your main accounts, credentials or private files, consider a separate test environment and a review by someone who can assess the installed components and security-sensitive code.
Agent access
An assistant connected to your email, files and browser concentrates access that an attacker would otherwise have to obtain separately. It’s worth considering the minimum permissions each task needs, a separate environment for experimental agents (I'd consider them all experimental at this stage) and a review of connections when the work ends, with attention to which ongoing functions would stop if access were removed.
Offline recovery codes
Where a service offers recovery codes, consider printing them and storing them securely offline rather than keeping your only copy in a password manager or cloud account, even an encrypted one. An independent copy can help if those systems are compromised or you lose access, though its usefulness depends on protection against theft, loss and damage.
A recovery plan
An encrypted backup kept disconnected when it isn’t in use can provide another route to recovery, especially if you have tested restoring files and know where the recovery keys are stored. Checking the recovery options for important accounts while you still control them can make a future incident much easier to handle.